What actually happens in the first 30 days if we switch to CHR?
We document before we change anything. Week one is discovery: every device, licence, password, vendor contract and backup job gets inventoried and handed back to you as written documentation you keep. Then we deploy monitoring and security agents, fix whatever the assessment flagged as urgent, and only afterwards take over day-to-day support. Your old provider stays live until cutover, so there is no window where nobody owns your systems. Full onboarding runs in weeks, not months.
Our last provider took days to answer a ticket. Who picks up, and how fast?
A CHR engineer, not a call tree or an offshore queue. Every ticket is triaged by severity the moment it lands, and each severity has a written response target and a named escalation path in your agreement, so an outage never sits in the same queue as a password reset. For critical incidents the response target is 15 minutes during business hours and 30 minutes after hours. On nights, weekends and holidays the 24×7 NOC answers every call, not a voicemail box, and on-call engineers respond to critical and high-priority incidents. Lower-priority requests queue for the next business day. If something is breaching its target, it escalates automatically instead of waiting for you to chase it.
What's actually included in the flat monthly fee, and what still gets billed separately?
Included: unlimited helpdesk support with 24×7 NOC coverage, monitoring, patching, security tooling, Microsoft 365 and cloud administration, backup management, and your quarterly technology reviews. Billed separately: hardware and third-party software licences at cost, and large one-off projects such as an office move, a server replacement or a cloud migration, quoted and approved before work starts. You will not receive an invoice for a busy support month, and there is no per-ticket or after-hours surcharge.
We already have an IT person and our own tools. Do we have to rip it all out?
No. Co-managed IT is a normal arrangement for us: your internal person keeps strategic control and the relationships, while CHR covers monitoring, helpdesk overflow, security operations and after-hours, whichever mix leaves the gaps covered. On tooling we assess what you own before recommending anything. If your existing backup or endpoint product does the job, we manage it. We only propose a replacement when there is a specific gap or a licence you are paying twice for, and we show you the reasoning.
If we get hit by ransomware at 2am, what actually happens?
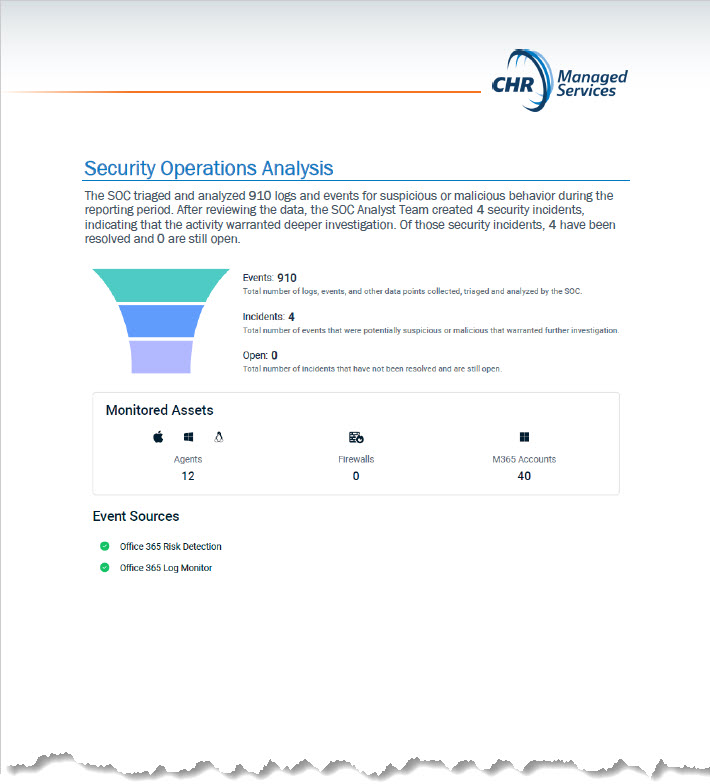
BYTE, our managed detection and response platform, is watching at 2am, and behind it are humans, not just alerting. Detection triggers containment first: isolate the affected endpoints to stop lateral spread, then assess scope, then begin recovery from backups we have been testing all along. You get a named incident lead and a communication line for the duration, and afterwards a written incident report, which is also what your cyber-insurance carrier and, depending on your industry, your regulator will ask for.
Who owns our data, licences and documentation if we decide to leave?
You do. All of it. Microsoft 365 and cloud tenants are registered to your business, not resold through us, so your licences and data stay yours regardless of who manages them. Network documentation, credentials and asset inventories are yours on request at any point in the relationship, not just at the end. If you leave, we hand over to your next provider in a documented transition. Nothing about the setup is designed to make leaving expensive.
Our client sent a security questionnaire and our auditor wants evidence. Can you produce it?
Yes. This is one of the most common reasons businesses call us. We support HIPAA, PCI and CMMC requirements, and because monitoring, patching, MFA, backup testing and security-awareness training are all running through our platforms, the evidence is already being produced as a by-product. That means we can supply patch and backup reports, access-control records, training completion and risk-assessment documentation instead of scrambling to reconstruct a paper trail the week an audit lands.
You're in Houston and we're not. Who shows up when hardware physically dies?
CHR is headquartered in Houston, Texas and supports clients across the United States through our remote service center and 24×7 monitoring operations. The honest answer is that the large majority of issues are resolved remotely, often before anyone reports them. For the work that genuinely needs hands on the equipment, on-site coverage is agreed up front, either scheduled visits or a vetted local partner, so it is defined in your plan rather than improvised during an outage.