We’ve Been Attacked. Now What?

What Small Businesses Should Do After a Cyber Incident
You think your business has been hit by a cyberattack. Maybe systems are locked, files aren’t accessible or something just isn’t right.
Now what?
For a small business without an internal cybersecurity team, the questions come quickly. Who do you call? Should you shut everything down? Can you keep doing business? Do customers need to know? What if there’s a ransom demand?
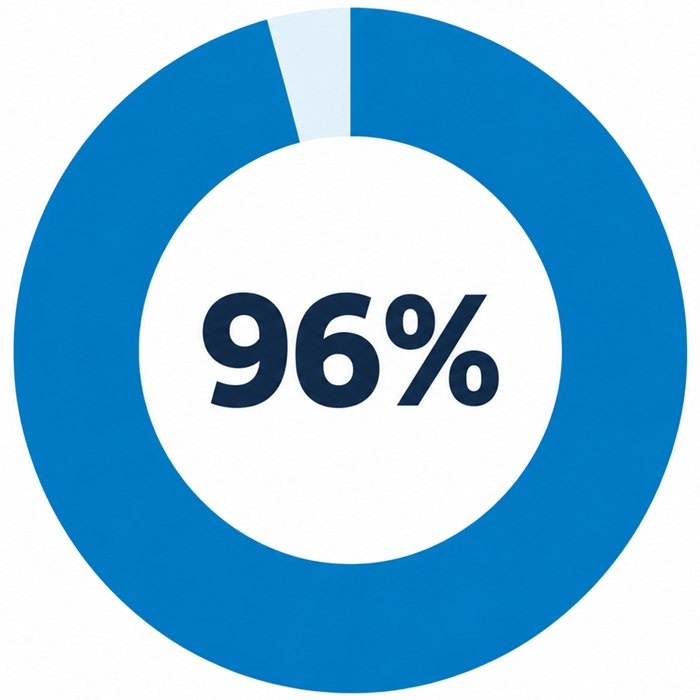
Small businesses can be particularly vulnerable because they often have fewer resources available to respond. Verizon’s 2026 Data Breach Investigations Report found that among ransomware cases where organization size was known, about 96% of victims were small- and medium-sized businesses (SMB). Ransomware was also present in 48% of all confirmed breaches analyzed in the report. The report also found that in the most severe 2.5% of SMB breach cases, losses exceeded 7% of annual revenue.


The first few decisions can make a difference. Here’s where to start.
What to do right away
The immediate priority is to contain the incident without destroying information that may be needed to understand what happened.
If you suspect your business has been attacked:
- Disconnect affected systems to help keep the threat from spreading.
- Preserve evidence. Don’t start deleting suspicious emails, files or messages.
- Get qualified cybersecurity help. If you don’t have an internal team, contact a managed cybersecurity provider with incident response expertise.
- Contact your cyber insurance carrier if you have one and follow the incident-reporting requirements in your policy.
- Don’t assume backups solve the problem. They may help restore systems, but information could have been accessed before the attack was discovered.
- Don’t make a quick decision about paying a ransom. The FBI does not support paying a ransom, and payment doesn’t guarantee your data will be recovered.
Once you’ve taken those first steps, the focus turns to understanding what happened and getting the business back on track.
Find out what was affected
Before restoring everything and moving on, you need to know the scope of the incident.
Which systems were compromised? Was sensitive information accessed or stolen? Are your backups secure? What can safely be brought back online?
Getting systems running again doesn’t necessarily mean the incident is over. Information may have been accessed before the attack was discovered, which can create additional obligations for the business.
This is where an experienced incident response provider can help determine what happened and what needs to happen next.
Can you keep doing business?
This is often one of the biggest concerns for a small-business owner. Customers are waiting. Employees need to work. Orders may need to be processed. Payroll still needs to happen.
The challenge is determining what can safely remain operational.
Bringing compromised systems back online too quickly can create more problems. Work with your response provider to identify essential functions that can continue safely while affected systems remain isolated or are restored.
Who needs to know?
The answer depends on the incident and the information involved.
There may be legal, regulatory or customer notification requirements if sensitive information was compromised. Your cyber insurance policy may also have specific reporting requirements.
Cyber incidents can be reported to the FBI through the Internet Crime Complaint Center (IC3). If ransomware is involved, getting professional guidance before responding to the attackers is important. The FBI does not support paying ransom because payment doesn’t guarantee that files will be restored or that stolen information won’t be released.
Once you’re back up, look at what went wrong
When the immediate crisis is over, don’t stop at restoring the systems.
Look at how the business handled the incident. Did everyone know whom to call? Were backups available and secure? Could you quickly determine which systems were affected? Did you know which parts of the business could safely keep operating?
Then look at the security gaps that may have contributed to the incident. A cybersecurity assessment can examine users, devices, networks, access controls, backups and security monitoring to identify areas that need attention.
The experience should also inform your incident response plan. The next time something looks wrong, your employees should know whom to contact and what steps to take.
Know who you’ll call before you need them
Most small businesses don’t need to build their own cybersecurity department. But they do need somewhere to turn when something goes wrong.
A managed cybersecurity provider can give a small business access to 24/7 monitoring, along with incident response expertise when a breach occurs, without requiring those resources to be maintained internally.
When a cyber incident happens, you don’t want to start searching for help while you’re trying to determine whether your business can operate.
Know who you’re going to call before you need to make the call.
Don’t have an internal cybersecurity team? CHR provides managed cybersecurity services with 24/7 monitoring and incident response expertise for small businesses. Contact us to request a free external vulnerability scan today.
Keep reading

A Cyber Scary Halloween
Halloween can be frightening for some – spooky decorations, scary costumes, not knowing what's lurking around the corner. What's interesting in our business is that Halloween and cybersecurity have…
Diving Deep into Phishing Scams
Phishing scams continue to be a prevalent and effective form to initiate a cyberattack, making it vital to recognize the threat it poses to your company. Without a…
4 Cybersecurity Considerations for When it Happens, Not If
Cybersecurity attacks are a little like shark attacks, most people know they’re possible, but they tend to happen to "other" people, so nobody prepares for them. But cybersecurity is a…