Don’t Let Cryptojackers Bleed You Dry
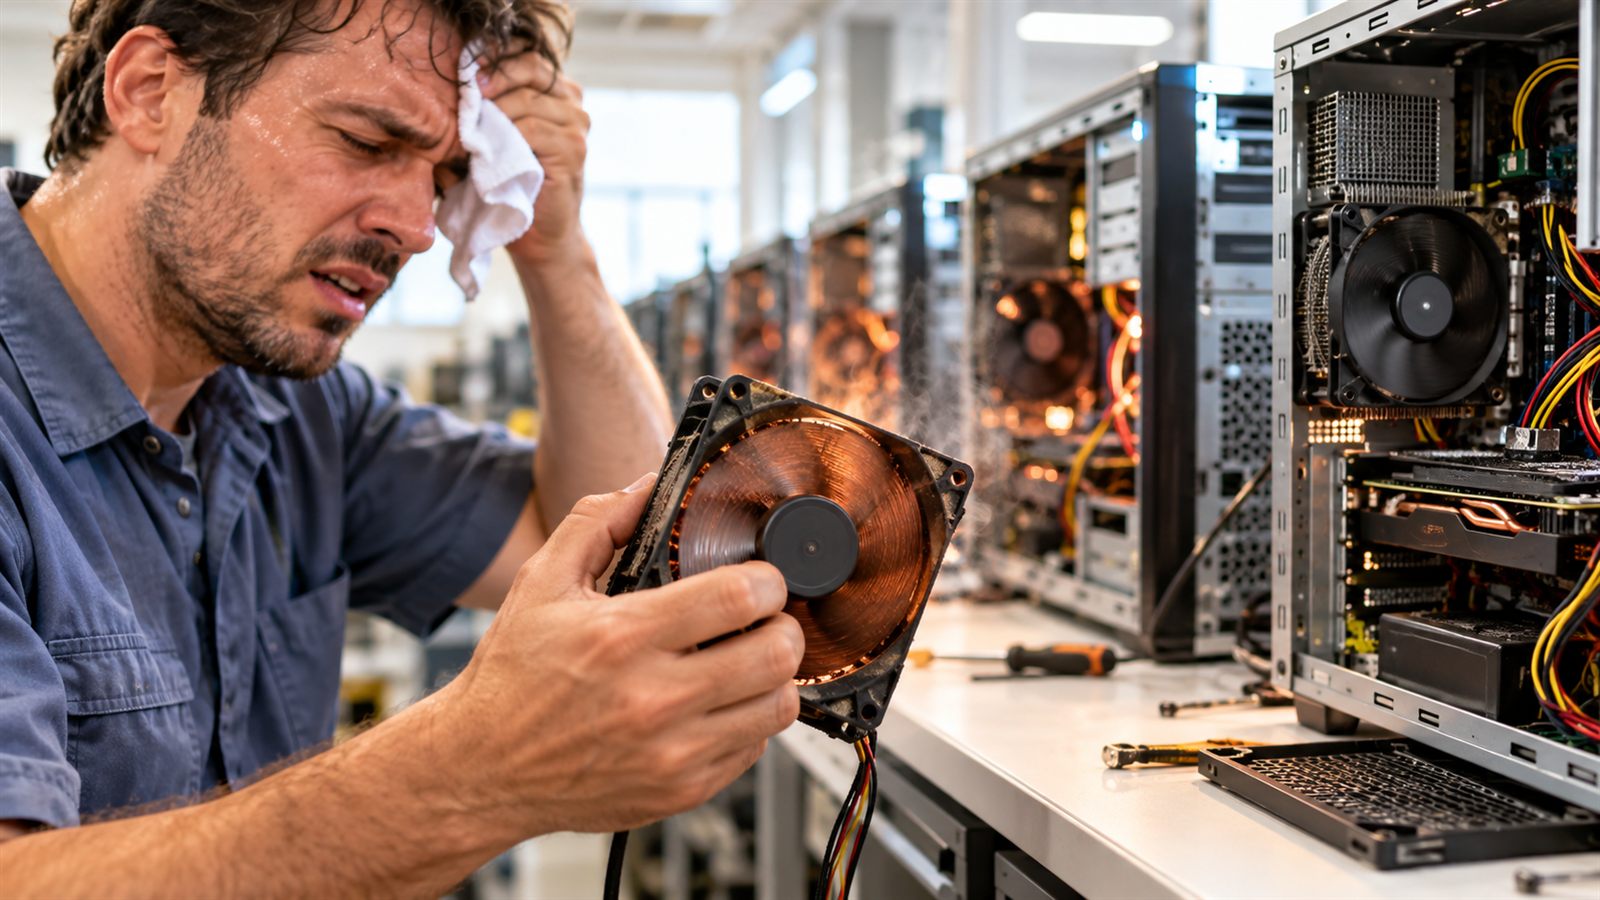
Cryptojacking is malware, or a hijacked system, that quietly uses your computing power to mine cryptocurrency for someone else. You pay for the electricity and the hardware wear. The attacker keeps the coins.
Cryptojacking made headlines years ago, when browser-based mining scripts and mining malware spread widely. It gets less attention now, and other threats, especially ransomware and stolen credentials, are bigger concerns for most businesses. But the idea has not gone away. Anyone who gets into your systems can try to use your computing resources, and that is worth watching for.
How it works
A miner needs processing power, and attackers prefer other people’s. Common ways they get it include:
- Exploiting unpatched servers and internet-facing applications.
- Guessing or stealing passwords for servers, remote access and cloud accounts.
- Abusing exposed or misconfigured services, including containers and cloud workloads.
- Phishing, where an employee opens a file or link that installs a miner.
Miners are often set up to look like normal system processes and to run in the background, so they can stay hidden for a long time.
Signs of unauthorized resource use
Whatever the attacker’s goal, the same warning signs apply. Look for:
- Servers or workstations running at high CPU or GPU use when they should be idle.
- Fans running constantly, devices running hot or batteries draining faster than usual.
- Systems that slow down for no clear reason.
- Unexpected jumps in your cloud bill, or new virtual machines and containers that nobody created.
- Unfamiliar processes, scheduled tasks or services.
- Unusual outbound connections, especially to destinations your business has no reason to contact.
Any one of these can have an innocent cause. Several together deserve a closer look.
How to protect your business
The defenses are the same basics that stop most attacks:
- Patch promptly, especially internet-facing systems.
- Use multi-factor authentication and strong, unique passwords, including for cloud and admin accounts.
- Limit what is exposed to the internet and review cloud settings regularly.
- Use endpoint protection that can detect mining software and suspicious processes.
- Monitor resource use and network traffic, and set alerts for unusual spikes and for cloud spending.
- Segment your network so an infected system cannot spread freely.
Monitoring is the key. A miner needs computing power, so it tends to show up as a pattern in usage long before anyone notices it by hand. CHR’s NOC monitoring watches your systems around the clock for exactly this kind of change. If you are not sure what is running on your network, request a free external vulnerability scan.
Keep reading
We’ve Been Attacked. Now What?
A small business without an internal cybersecurity team has questions the moment an attack hits. Here is what to do first, how to find out what was affected…

A Cyber Scary Halloween
Halloween can be frightening for some – spooky decorations, scary costumes, not knowing what's lurking around the corner. What's interesting in our business is that Halloween and cybersecurity have…
Diving Deep into Phishing Scams
Phishing scams continue to be a prevalent and effective form to initiate a cyberattack, making it vital to recognize the threat it poses to your company. Without a…